Agentic Apps vs Chatbot Agents: Which Wins for Enterprise AI?
Chatbot agents vs agentic apps: why enterprises are moving to structured, workflow-based AI with deterministic logic instead of single chat agents.
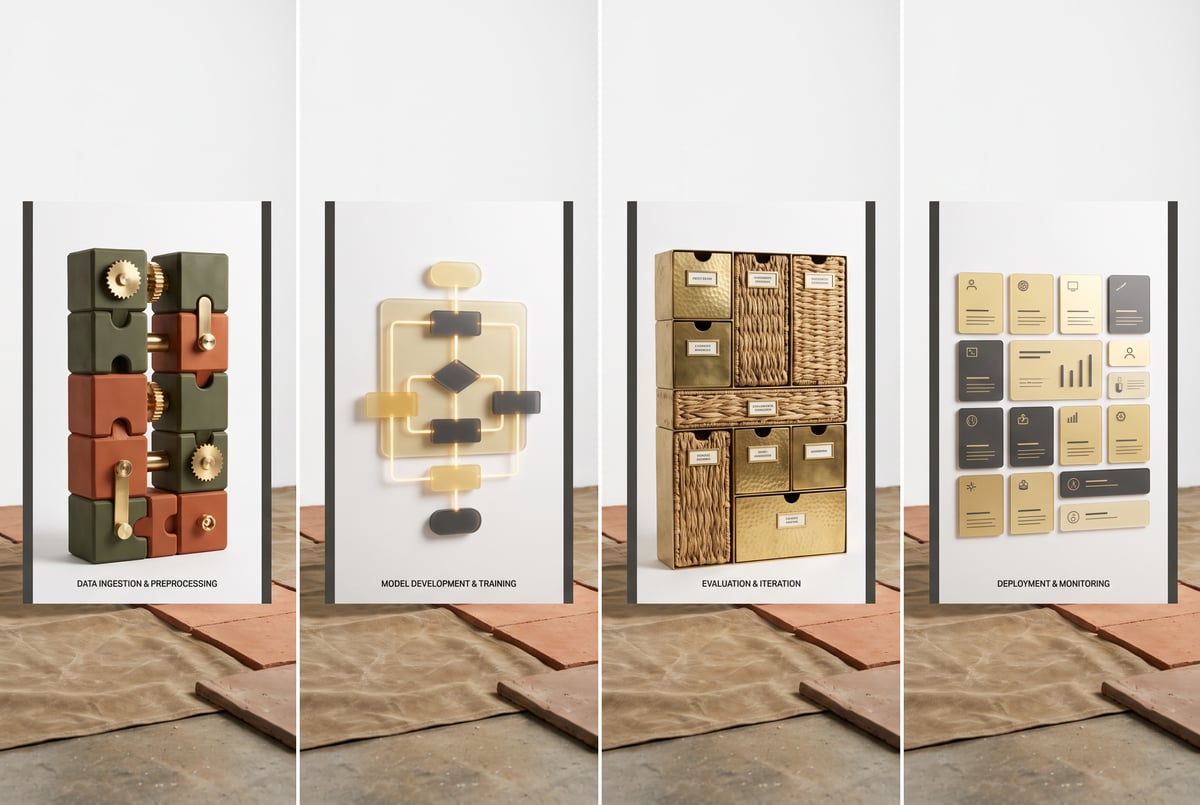
What’s the difference between a chatbot agent and an agentic app?
A chatbot agent is a single AI agent wrapped around a chat window: you type a request, it reasons, it replies. An agentic app is a structured application built around a business outcome, where one or more agents act as tools inside deterministic workflows, with visual components, permissions, and triggers controlling how and when the AI gets invoked. The chatbot puts the model in charge of the whole interaction. The agentic app puts the workflow in charge and calls the model only where it adds value.
TL;DR
- Chat-only agents work well for personal tools and single-use-case automation, but they struggle to scale inside larger business processes because the agent itself becomes the entire application.
- Agentic apps flip the build order: start with the business outcome (like managing a team’s development or answering HR policy questions), then decide where agents fit inside the workflow.
- Deterministic workflows wrap every LLM call with code nodes, conditionals, and context injection, so the model only contributes where flexibility is actually needed.
- Policies replace loose RAG for anything mission critical: instead of letting an agent search and summarize a document on the fly, the content gets codified into tested functions with strict inputs and outputs.
- Visual output matters: agentic apps render results as dashboards, PDFs, or slide decks instead of walls of chat text, which cuts down on the mental overhead of parsing every response.
- Oracle AI Agent Studio was used as the reference implementation in this comparison, building agentic apps by starting with workflows and attaching UI components and agents to them.
- Security and scoping happen at the workflow level, covering who can trigger a workflow, what identity it runs under, and exactly which functions an agent can call.
Seven tools to build an app. Or just Remy.
Editor, preview, AI agents, deploy — all in one tab. Nothing to install.

Why are enterprises moving away from single chat agents?
The appeal of a chat agent is obvious: it’s fast to build, flexible, and can handle a wide range of requests without much upfront design. That’s exactly why it became the default pattern over the last couple of years. But flexibility is also the weakness. When an agent is the entire automation, every output is probabilistic. For a personal second brain or a coding assistant, that’s an acceptable tradeoff. For a business process where outputs need to be consistent, auditable, or tied to compliance, it isn’t.
The core problem is that teams often start by asking “what can we automate with an agent?” instead of “what business outcome are we trying to deliver?” That ordering matters. Starting with the agent tends to produce technology-driven projects that look impressive in a demo but don’t map cleanly onto how someone actually does their job. Starting with the outcome, like giving a manager one view into how engaged their team is with professional development, forces the build to stay grounded in a real workflow, with agents added only where they solve a specific piece of it.
How do agentic apps actually work?
An agentic app is organized around a single view tied to a role or outcome, not around a chat box. Inside that view, each interactive component (a summary, a chart, a “send follow-up email” button) is backed by its own workflow. The workflow is the deterministic skeleton: it loads context, runs conditional logic, calls code nodes for formatting, and invokes an LLM only at the specific step where reasoning or generation is needed.
This matters because it gives builders guarantees that pure chat agents can’t. Context can be loaded the same way every time. The right model can be selected based on a conditional. Outputs can be reformatted before they ever reach the user. None of that depends on the agent “deciding” to do it correctly on a given run. The workflow enforces it.
In practice, this looks like building the workflow first, testing it in isolation (including checking raw JSON output before it’s wired into a UI), and only then attaching it to a visual component in the app. The chat interface doesn’t disappear entirely. Users can still ask follow-up questions. But it sits alongside structured components rather than being the only interface.
Why does determinism matter more than flexibility in enterprise settings?
LLMs are good at looking at a messy problem and figuring out a reasonable path to a solution. That’s valuable, but it’s also a liability when the cost of being wrong is high. Enterprise workflows often have hard requirements: specific context must always load, specific tools must always be scoped to the task, and certain answers (like a vacation policy) can’t be approximately right, they have to be exactly right.
This is the reasoning behind replacing retrieval-augmented generation (RAG) with codified policies for sensitive or high-stakes information. RAG retrieves and summarizes chunks of a document on the fly, which is usually accurate but not guaranteed to be. For something like an HR handbook’s leave policy, “usually accurate” isn’t a good enough bar. The alternative demonstrated in Oracle AI Agent Studio is to upload the source document and convert its guidelines into functions, each with generated source code, test cases, and strict input/output definitions. The agent then calls those functions instead of searching the raw document, which produces a consistent answer every time rather than a probabilistic one.
The broader industry pattern here is converging on the same idea: push as much determinism as possible into the workflow layer, and reserve the LLM for the steps that genuinely need language understanding or generation, like classifying a question or drafting a message.
How do agentic apps handle security and permissions?
Security in an agentic app gets enforced at two levels. First, at the agent level, through policies that define exactly which functions an agent can call and what inputs and outputs are valid. This keeps an agent from having broader capabilities than the task requires. Second, at the workflow level, where access can be scoped by who is allowed to trigger a given workflow and what identity the workflow runs under as it executes.
This granularity is hard to replicate in a pure chat-agent setup, where the agent typically has a fairly broad set of tools and relies on prompting or guardrail instructions to behave correctly. In an agentic app, the permission boundary is structural, not just instructional. Workflows can also be triggered by things other than a user clicking a button in the app, such as an incoming email, which extends the same policy and workflow logic to automated, event-driven processes.
Is building an agentic app worth it over a simple chatbot?
For personal productivity tools, side projects, or lightweight automation, a single chat agent is often enough and faster to stand up. The tradeoff becomes worth addressing once the stakes rise: when outputs need to be reliable every time, when multiple people with different permissions need to use the same system, or when the process being automated has several distinct steps that benefit from different handling (classification, formatting, routing to different models). At that point, the chat agent model tends to become a bottleneck or a risk, and restructuring the work as a workflow-driven app with agents as one component pays off in reliability and control.
Visual output is part of that payoff too. A chat response works fine for a quick question, but for anything more comprehensive, like a team engagement summary or a risk rundown, a dashboard, PDF, or slide deck is far easier to scan and act on than a long block of generated text, especially if that kind of summary gets produced repeatedly throughout a workday.
Frequently Asked Questions
What is an “agentic app” as opposed to an AI agent?
An agentic app is a full application built around a specific business outcome, where AI agents are embedded as tools inside deterministic workflows. An AI agent on its own is typically a single conversational interface where the model drives the entire interaction.
Why is RAG not always sufficient for enterprise AI agents?
RAG retrieves and summarizes relevant chunks of a document, which is usually accurate but not guaranteed. For policies or rules where the answer must be correct every time, codifying the source material into tested functions with strict inputs and outputs produces more reliable results than on-the-fly retrieval.
Other agents start typing. Remy starts asking.
Scoping, trade-offs, edge cases — the real work. Before a line of code.
Does an agentic app still include a chat interface?
Yes. Chat remains available for follow-up questions and open-ended requests, but it sits alongside structured, pre-built components (dashboards, buttons, generated documents) rather than being the only way to interact with the system.
Who builds agentic apps, developers or business users?
Platforms like Oracle AI Agent Studio are designed so non-technical business users can describe a desired outcome and get a working agentic app with workflows and components already configured, while professional developers can also build the same kind of structure directly in code.
What makes a workflow “deterministic” if it still calls an LLM?
The LLM call is just one step surrounded by fixed logic: context loading, conditionals, code-based formatting, and classification steps that don’t depend on model output. This limits the model’s role to the specific point where flexible reasoning or generation is actually needed, rather than letting it control the entire process.